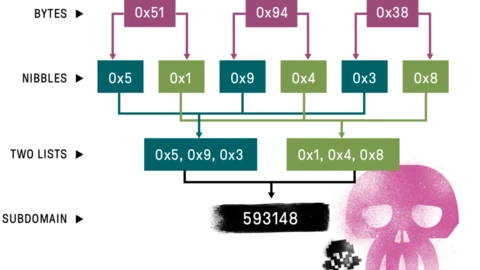
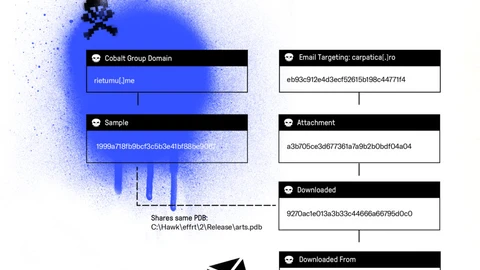
Executive Summary Cobalt Group (aka TEMP.Metastrike), active since at least late 2016, have been suspected in attacks across dozens of countries. The group primarily targets...
Arbor ASERT has uncovered a new class of SSDP abuse where naïve devices will respond to SSDP reflection/amplification attacks with a non-standard port. The resulting flood of UDP...
Key Findings ASERT researchers discovered Kardon Loader being advertised on underground forums. Kardon Loader features functionality allowing customers to open their own botshop...
Executive Summary Mirai, seen as revolutionary for malware that targets the Internet of Things (IoT), has wrought destruction around the globe and popularized IoT based malware...
Written by Roland Dobbins, ASERT Principal Engineer and Matt Bing, ASERT Security Analyst. In this article: SSDP Diffraction Attacks aren’t new; they’ve been observed in the wild...
NETSCOUT SYSTEMS, INC. EMPLOYEE/CANDIDATE PRIVACY NOTICE Effective December 6, 2019 Your privacy is important to us. This notice describes how NetScout Systems, Inc. a Delaware...
About Partnerships At NETSCOUT our Channel partners are a vital part of the NETSCOUT family, and critical to our success. Our partner programs are specifically designed to support...
Overview ASERT recently identified a campaign targeting commercial manufacturing in the US and potentially Europe in late 2017. The threat actors used phishing and downloader(s) to...
Key Findings A threat actor using the well-known banking malware Panda Banker (a.k.a Zeus Panda, PandaBot) has started targeting financial institutions in Japan. Based on our data...
Authors: Dennis Schwarz and Jill Sopko Special thanks to Richard Hummel and Hardik Modi for their contributions on this post. Figure 1: Pakistan themed decoy document Key Findings...
Last week, after Akamai confirmed a 1.3Tbps DDoS attack against Github, I published a blog that looked at the last five years of reflection/amplification attack innovation. I hope that it provides a helpful backgrounder on how we got here to the terabit attack era.
Special thanks to Hardik Modi, Steve Siadak and Roland Dobbins for their contributions on this post. Reflection amplification is a technique that allows cyber attackers to both...
February 20, 2018: This blog has been amended since it was originally published on February 15, 2018. This version removes the association with the APT group responsible for the...
Authors: Pete Arzamendi, Matt Bing, and Kirk Soluk. Satori, the heir-apparent to the infamous IOT malware Mirai, was discovered by researchers in December 2017. The word "satori"...
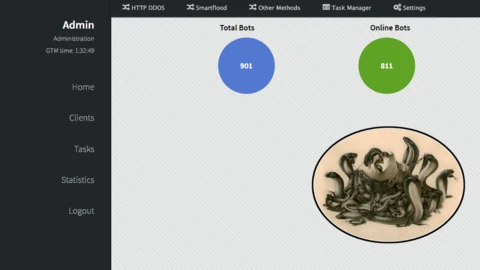
Executive Summary MedusaHTTP is a HTTP-based DDoS botnet written in .NET, that surfaced in early 2017. MedusaHTTP is based off of MedusaIRC which leveraged IRC for its command and...